A full assessment once a year, plus a reassessment whenever a new product, payment method or market launches. Continuous monitoring (stage 6) runs the whole time in between.
Fraud risk assessment framework: Six stages, scoring model and template
A six-stage fraud risk assessment framework: scope, risk identification, 1-5 scoring, control mapping, residual risk and real-time monitoring, with a template.
On this page
- Established frameworks for fraud risk assessment
- How industry standards fit into the assessment
- What a fraud risk assessment framework gives you
- The six-stage fraud risk assessment framework
- Building a fraud risk scoring model
- Fraud risk assessment template
- Common mistakes
- Where to start
- Frequently asked questions
Occupational fraud costs organisations an estimated 5% of annual revenue, according to the Association of Certified Fraud Examiners (ACFE). Not every fraud risk deserves the same attention, and the point of a fraud risk assessment is to work out which ones do.
The framework below shows where fraud is most likely, measures what it would cost, and ranks controls on evidence rather than assumption. It runs from scope and risk identification through scoring, control mapping and residual risk to continuous monitoring, with a scoring model, a register template and a worked example.
Established frameworks for fraud risk assessment
Several published frameworks cover parts of the job. Few organisations follow one from start to finish; most combine pieces to fit their risk profile, regulatory obligations and business model.
The figure below shows where each adds the most value.
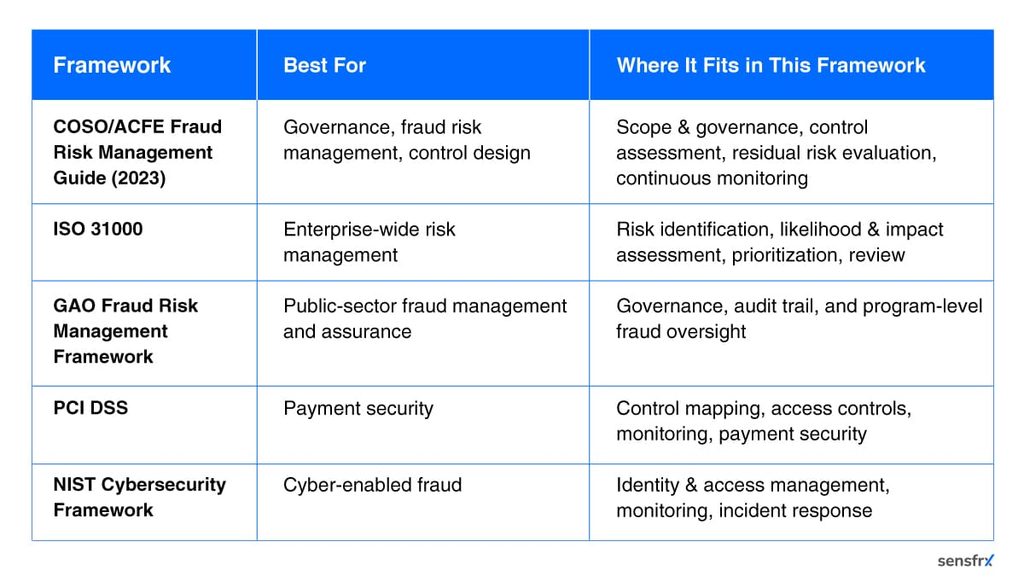
This guide does not replace them. It applies their structure to a faster, transaction-heavy environment and fills in the scoring and monitoring detail they leave abstract.
How industry standards fit into the assessment
Each standard strengthens a different stage:
- COSO/ACFE Fraud Risk Management Guide (2023): governance, responsibilities, control evaluation and residual risk monitoring.
- ISO 31000: a structured method to identify, assess, prioritise and review risks.
- PCI DSS: payment security through access controls, monitoring, logging and control mapping.
- NIST Cybersecurity Framework (CSF): identity and access management, continuous monitoring and incident response for cyber-enabled fraud.
Used together they give an assessment that satisfies the auditor and still works day to day.
What a fraud risk assessment framework gives you
It moves the business from reacting to incidents to managing fraud risk ahead of them. With risks identified, scored and ranked you can:
- Put resources on the highest-risk areas instead of spreading them evenly
- Find control gaps and fix them
- Cut financial loss, regulatory exposure and reputational damage
- Show compliance with COSO, ISO 31000 and sector regulation
- Make decisions on one consistent, risk-based basis across business units
- Adjust to new fraud patterns through regular monitoring and reassessment
The six-stage fraud risk assessment framework
The six stages, and what each one produces:
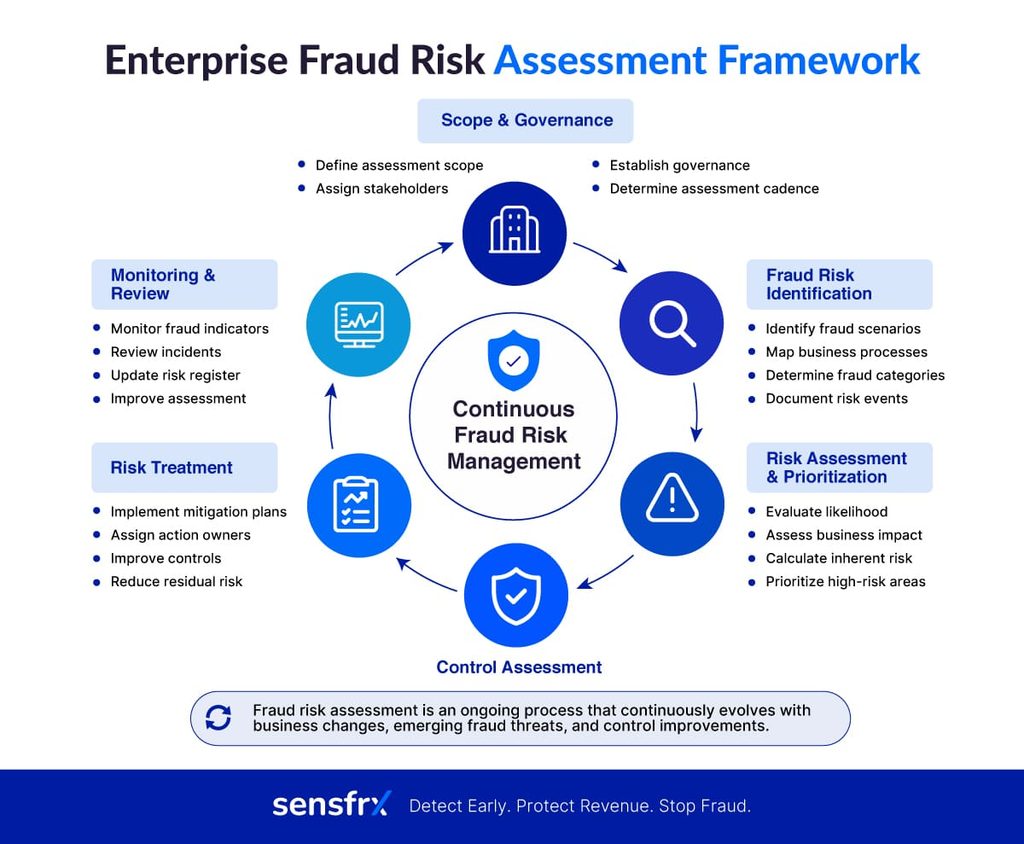
Step 1: Scope and governance
Before you list a single risk, decide:
| Question | What to decide |
|---|---|
| Scope | Which business units, subsidiaries, departments, business processes, third parties, or geographic locations are included in the assessment (e.g., procurement, payroll, finance, sales, HR, IT, supply chain). |
| Ownership | Who is responsible for leading the assessment (e.g., Enterprise Risk Management (ERM), Internal Audit, Compliance, Fraud Risk Management, or a cross-functional committee with Finance, Legal, HR, IT, and Operations). |
| Cadence | How often the assessment will be performed (e.g., annually or semi-annually) and the events that trigger reassessment, such as mergers and acquisitions, new business initiatives, significant organizational changes, fraud incidents, regulatory changes, or implementation of new systems. |
| Reporting Line | Who reviews and approves the assessment results (e.g., executive management, Risk Committee, Audit Committee, or Board of Directors), how findings are reported, and who has the authority to approve mitigation plans and control improvements. |
Step 2: Risk identification
List every plausible fraud scheme, not just the ones that have already happened, and group them by business process so nothing is missed:
| Business Process | Common Fraud Risks |
|---|---|
| Procurement | Vendor fraud, kickbacks |
| Payroll | Ghost employees |
| Accounts Payable | Duplicate payments |
| Accounts Receivable | Payment diversion |
| Expense Management | Expense reimbursement fraud |
| Sales | Revenue manipulation |
| Inventory | Theft and inventory shrinkage |
| Third-party Management | Supplier collusion |
| IT | Identity misuse and privileged access abuse |
Most published frameworks stop at the first two rows. For an ecommerce or fintech business the last two usually carry more financial exposure.
Step 3: Likelihood and impact scoring
Score each risk on two 1-5 scales:
| Score | Likelihood | Impact |
|---|---|---|
| 1 | Rare, no history of this in the business | Negligible financial or reputational cost |
| 2 | Unlikely, isolated past incidents | Minor cost, easily absorbed |
| 3 | Possible, occurs occasionally in the industry | Moderate cost, noticeable in a quarterly report |
| 4 | Likely, has occurred more than once | Significant cost, affects margin or requires disclosure |
| 5 | Almost certain, ongoing or recurring | Severe, threatens processor relationships, licensing, or solvency |
Multiply likelihood by impact for a score out of 25. That gives you a ranked list.
Note: the 1–5 model is a starting point, not a standard. Set the criteria and thresholds to your own risk appetite, business model and regulatory requirements.
Step 4: Control mapping
For every risk above a chosen threshold (12 or higher, say), map the existing controls against it:
| Risk | Existing Control | Control Type | Gap Identified |
|---|---|---|---|
| Procurement fraud (e.g., fictitious vendors, kickbacks) | Vendor onboarding and approval process | Preventive | No periodic vendor due diligence or conflict-of-interest reviews |
| Payroll fraud (e.g., ghost employees, unauthorized payroll changes) | HR approval workflow and payroll reconciliation | Detective | No segregation of duties or automated payroll exception monitoring |
| Expense reimbursement fraud | Manager approval for expense claims | Detective | No automated duplicate expense detection or receipt validation |
| Financial statement fraud | Management review and journal entry approvals | Preventive | No independent review of high-risk journal entries or unusual adjustments |
| Third-party/vendor fraud | Third-party due diligence during onboarding | Preventive | No ongoing monitoring of vendor risk or periodic compliance reviews |
| Asset misappropriation | Asset inventory records and periodic audits | Detective | Physical inventory counts performed infrequently and asset tracking is manual |
| Unauthorized system access | Role-based access control (RBAC) and password policy | Preventive | User access reviews are not conducted regularly; privileged accounts are not continuously monitored |
| Bribery and corruption | Code of conduct and ethics training | Preventive | Gifts, hospitality, and third-party payments are not centrally monitored or reviewed |
Step 5: Residual risk and control testing
With controls mapped, test whether they work, not whether they exist on paper.
| Test question | Why it matters |
|---|---|
| Is the control operating as designed right now? | A rule that was configured correctly a year ago may have been quietly disabled or bypassed |
| Does the control catch the scheme at the volume fraud actually occurs at? | A manual review process that works at 10 cases a day breaks down at 500 |
| What’s the residual risk score after the control is applied? | This is the number that should drive investment decisions, not the inherent risk score |
Step 6: Continuous monitoring and real-time scoring
This is the stage that matters most for transaction fraud.
The components:
| Component | Role |
|---|---|
| Event stream | Every login, checkout, or account change generates a scoreable event |
| Signal enrichment | Device fingerprint, IP reputation, behavioral pattern, and historical account data are attached to the event |
| Real-time scoring | A weighted or model-based score is generated in milliseconds |
| Action routing | Score thresholds route the event to auto-approve, step-up verification, manual review, or block |
| Feedback loop | Confirmed fraud and confirmed false positives are fed back to retrain the scoring logic |
Here the periodic assessment becomes an operating system for fraud risk instead of a document filed until next year's audit.
Building a fraud risk scoring model
A scoring model turns the likelihood and impact exercise into something that runs against live data. A simple weighted model looks like this:
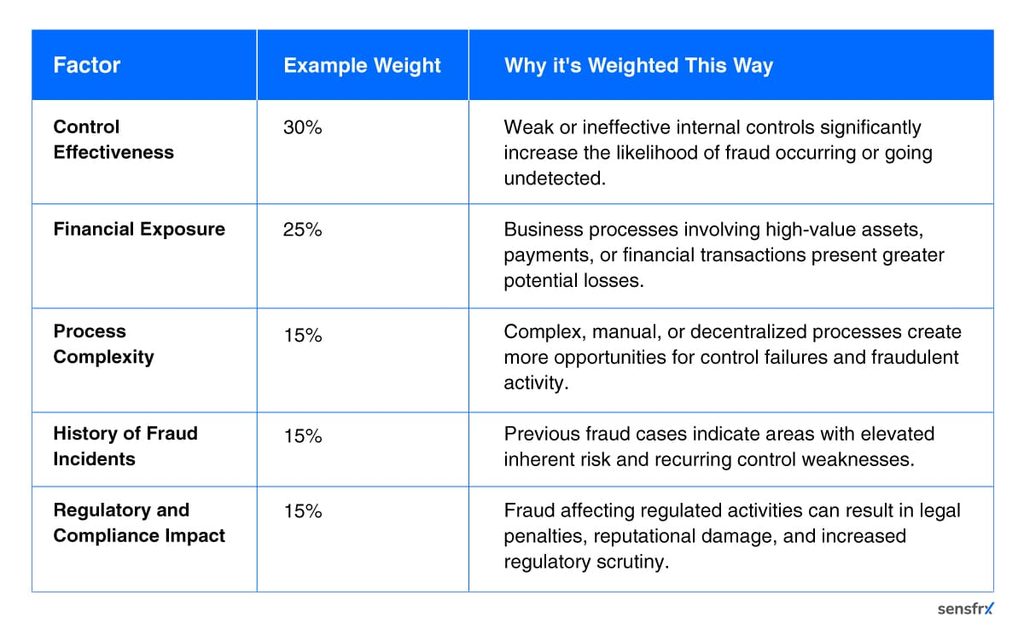
A static weighted model is a reasonable start. Machine-learning scoring learns the weights and interactions from labelled fraud history instead of having them set by hand, and updates as new patterns appear. The stages do not change; only how stages 3 and 6 are run.
Fraud risk assessment template
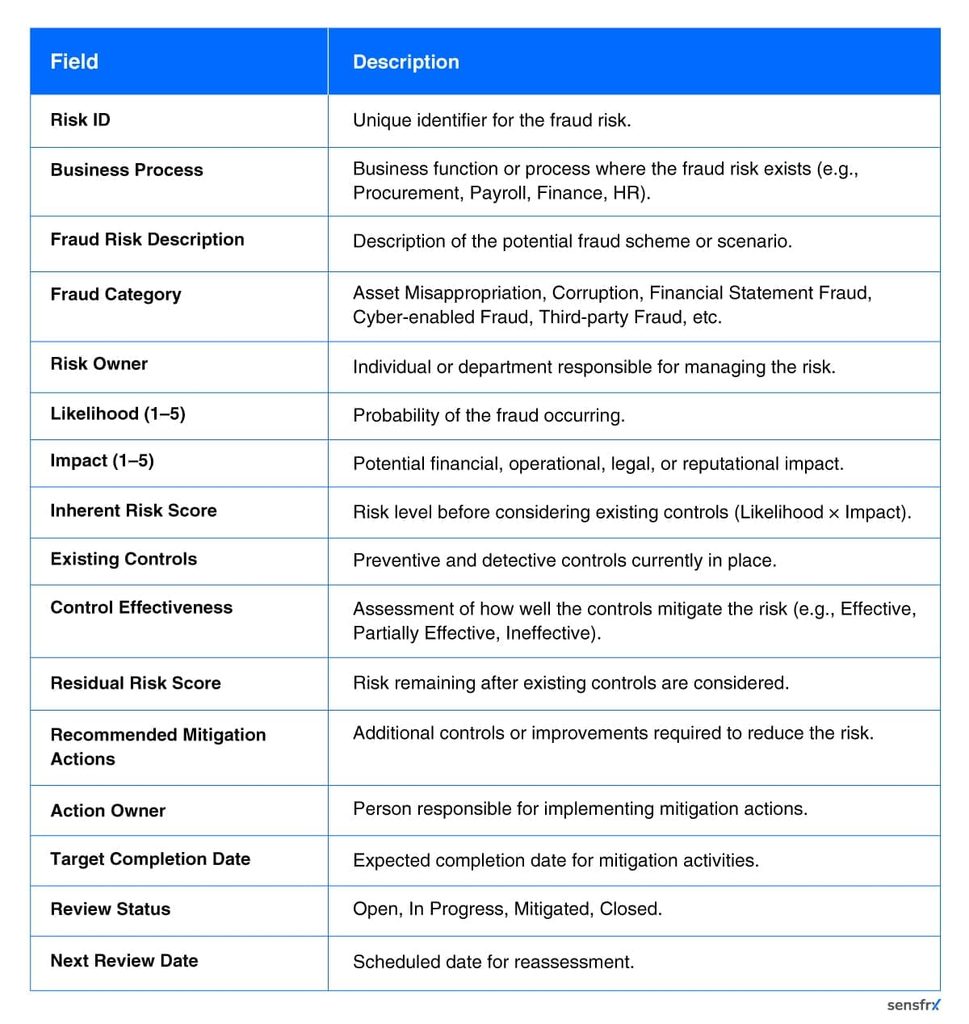
A copy-ready structure for a risk register:
It records inherent risk, the controls in place, residual risk and mitigation status for each process, in one structure that works across business units.
Example
| Risk ID | Business Process | Fraud Risk | Inherent Risk | Existing Controls | Residual Risk | Status |
|---|---|---|---|---|---|---|
| FR-001 | Procurement | Fictitious vendor creation resulting in fraudulent payments | 20 | Vendor approval workflow, segregation of duties | 10 | In Progress |
| FR-002 | Payroll | Ghost employee fraud | 16 | HR approval, payroll reconciliation | 8 | Mitigated |
| FR-003 | Expense Management | Duplicate or falsified expense reimbursements | 15 | Manager approval and expense policy | 9 | Open |
| FR-004 | Finance | Unauthorized journal entry manipulation | 20 | Journal approval workflow and audit logs | 12 | Open |
Keep it in a shared, versioned sheet so residual scores can be compared quarter over quarter instead of starting fresh each cycle.
Worked example: An enterprise assessment
A manufacturer operating in three countries runs its annual assessment across procurement, payroll, finance and third-party vendor management. After scoring likelihood, impact and existing controls, three risks rank highest:
- Procurement fraud (inherent risk score 20): weak vendor due diligence and little oversight of supplier onboarding.
- Payroll fraud (inherent risk score 16): payroll changes rely on manual approvals with no independent review.
- Expense reimbursement fraud (inherent risk score 15): inconsistent checking of employee expense claims.
Approval workflows exist, but they are manual and do not detect fraud. The company adds vendor verification, segregation of duties for payroll changes, automated duplicate-expense checks and quarterly control testing.
Residual scores fall to 10, 8 and 9. Procurement fraud stays high priority and goes to the Risk Committee quarterly; payroll and expense fraud move into Internal Audit's routine control monitoring.
The assessment did its job: it ranked the risks, fixed the controls and put the money where the exposure was.
Common mistakes
| Mistake | Consequence |
|---|---|
| Treating the assessment as an annual compliance exercise only | Misses fast-moving digital fraud that changes shape within weeks |
| No defined reassessment trigger | New product launches or market expansions go live without a fraud risk review |
| Focusing only on internal fraud categories | Transaction and account-level fraud, often the larger dollar exposure, goes unscored |
| No cross-functional input | Product and engineering teams aren’t involved, so control gaps in checkout or onboarding flows go unnoticed |
| No feedback loop from monitoring back to the risk register | Confirmed fraud patterns never update the likelihood or impact scores that drove the original assessment |
Turning standards into action
Whichever framework you follow, the assessment should answer five questions:
- Are we assessing the fraud risks that matter most to the business?
- Do the existing controls reduce those risks?
- Which high-risk areas need mitigation now?
- How will we monitor fraud risk as the business, the technology and the attackers change?
- Who is accountable for reviewing, updating and reporting it?
If the assessment answers these every cycle, you have a repeatable fraud risk programme rather than a compliance artefact.
Where to start
A fraud risk assessment framework earns its keep when it changes what the business does, not what it documents. COSO and ISO 31000 supply the governance; a scoring model and continuous monitoring supply the part that runs every day.
Sensfrx is built for stage 6. It combines device intelligence, behavioural signals, IP and email analysis and real-time risk scoring, so the risks you identified in the assessment become controls at signup, login and payment.
See Sensfrx pricing and run the scoring on your own traffic; the free plan is enough to start.